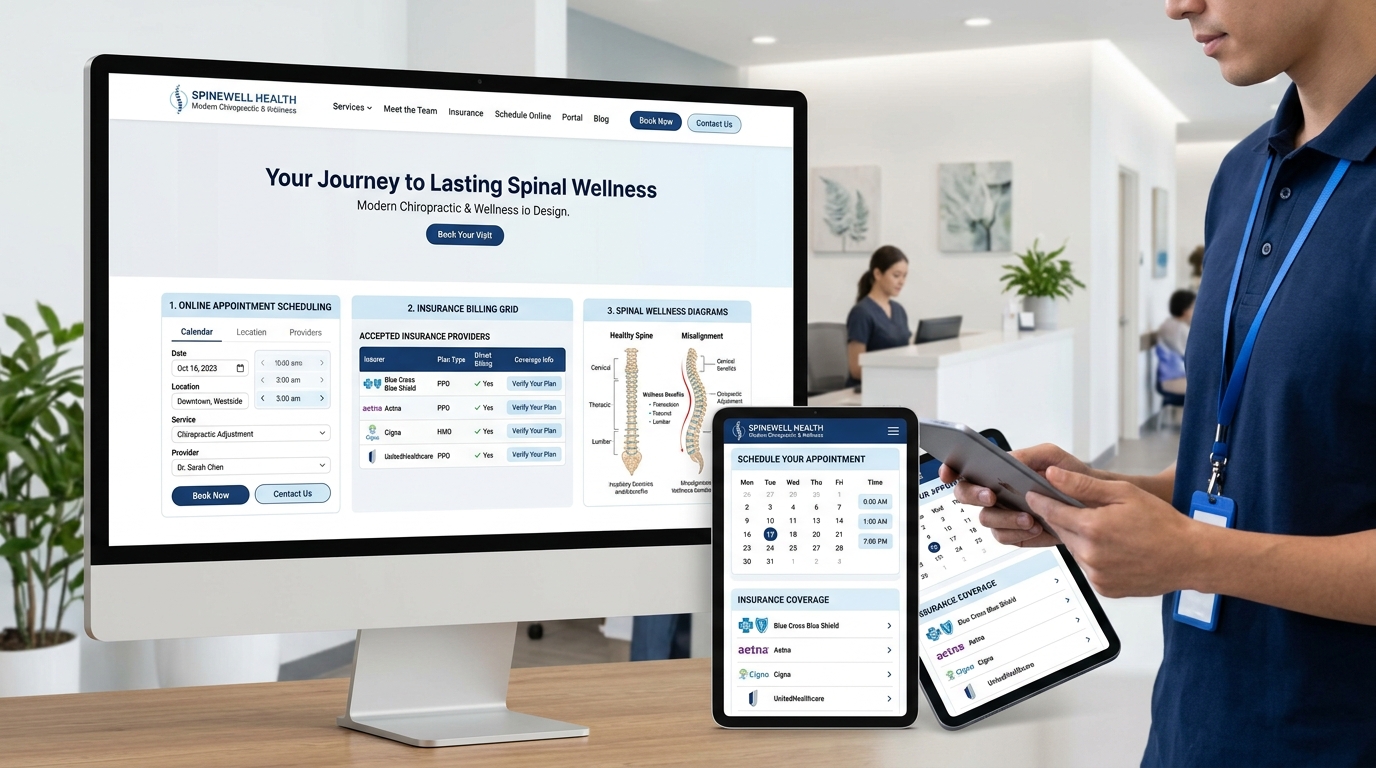
When a patient is searching for a local physician, dentist, or chiropractor, their experience on your practice website forms their first impression of your clinical care. They expect an immediate, professional, and secure digital environment.
However, as revealed in our analysis of Medical and Dental CMS Vulnerabilities, traditional dynamic websites operating on legacy PHP and MySQL platforms create continuous cybersecurity vulnerabilities and regulatory exposure for healthcare providers.
To permanently eliminate these risks, leading medical practices are transitioning to Modern Edge-Hosted Static Infrastructure.
Why Dynamic CMS Architecture Fails Healthcare Providers
In a legacy website setup, every visitor request initiates an active server execution cycle:
- The Visit: A patient clicks to view office hours or doctors’ bios.
- Server Execution: The host server spins up an active PHP runtime process.
- Plugin Pipeline: Dozens of unverified plugins execute code on the server.
- Database Connection: The server connects to a live MySQL database.
This dynamic pipeline creates a massive attack surface. If any single plugin contains a security bug, automated botnets can hijack your domain, inject spam redirects, or access stored form submissions.
The Modern Alternative: Pre-Rendered Edge Architecture
Modern edge architecture takes a fundamentally secure approach by shifting all page compilation to build time:
- Immutable Static Delivery: Every service page, doctor profile, location guide, and patient resource is pre-compiled into clean, static HTML and lightweight assets during deployment.
- Distributed Global Edge CDN: Assets are deployed across a distributed global edge network, positioning copies across hundreds of secure points of presence worldwide.
- Zero Runtime Execution: When a patient loads your website, the edge network delivers the pre-built file in milliseconds. There is no active PHP server to exploit, no WordPress core to compromise, and no database exposed to the web.
Decoupled, HIPAA-Aligned Appointment & Intake Workflows
One of the greatest liabilities for practice owners is storing patient intake messages on standard web servers. In a modern edge architecture, interactive workflows are completely decoupled:
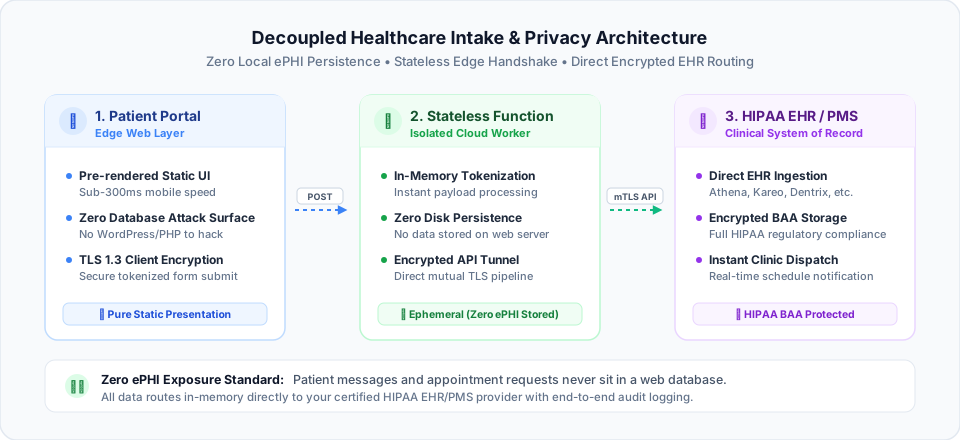
- Stateless Edge Processing: When a patient submits an appointment request, an isolated serverless edge function processes the submission in memory without writing data to the web host.
- Direct EHR/PMS Routing: Form submissions route directly into your HIPAA-compliant Practice Management System (PMS), Electronic Health Record (EHR), or encrypted intake gateway via secure webhooks.
- Zero Local ePHI Footprint: No patient symptoms, phone numbers, or insurance card images are ever stored on the public website filesystem, completely removing the primary cause of clinical web data breaches.
Architectural Comparison: WordPress vs. Modern Edge
| Security & Performance Metric | Monolithic Dynamic CMS | Modern Edge Architecture |
|---|---|---|
| Server Runtime | Active PHP server & live MySQL database | Pre-rendered static assets on global edge CDN |
| Vulnerability Attack Surface | Critical (plugins, themes, REST routes) | Zero (no server-side scripts to exploit) |
| Patient Data Storage | Stored locally in web database | Decoupled, encrypted routing directly to EHR/PMS |
| Mobile Load Speed | 3.0s – 6.5s (database latency) | 150ms – 400ms (instant mobile delivery) |
| Uptime Guarantee | Vulnerable to crashes & plugin breaks | 100% resilient across distributed edge |
| Ongoing Maintenance | Weekly plugin updates & vulnerability scans | Zero server, CMS, or database patching |
Practice Growth & Operational ROI
Migrating your clinical practice to modern edge infrastructure delivers immediate clinical and commercial returns:
1. Sub-Second Mobile Performance Boosts Local SEO
Patients in urgent need of care search on mobile devices. Fast, sub-400ms page loads dramatically improve Core Web Vitals, elevating your practice in Google Maps and local 3-Pack rankings.
2. Elimination of Fake Update & Redirect Threats
Because edge-hosted static files cannot be altered at runtime, automated malware campaigns (like Balada Injector or ClickFix) cannot inject malicious scripts or redirect your patients.
3. Reduced IT Costs & Total Peace of Mind
Practice owners and office managers no longer have to worry about plugin update failures breaking online booking forms right before a busy weekend.
Elevate Your Practice’s Digital Infrastructure
Protect your patients, eliminate administrative headaches, and secure your clinical practice with modern decoupled edge infrastructure.
Contact us to schedule a consultation and learn how an edge migration can protect your practice.